Tuesday, October 31, 2006

Back from Cambodia

Finally my long holidays ended, I have very good time while in Cambodia as well as Bangkok and amazed with all the ancient buildings and its histories. Anyway I'm back on track now, the first interesting stuff that I read is the interview of OpenBSD developers regarding OpenBSD 4.0. You can check it out at here.

After finish reading it, now I strongly believe that OpenBSD is considered to be one of most robust and best platform offered to build VPN, Routing and Firewalling solution ever.

Kudos to all OpenBSD developers for their decent work!!!!!

Enjoy :]

Saturday, October 21, 2006

Festival Moments

To all the people out there, I know you are in good mood - happy Deepavali, happy AidilFitry and happy holidays!!!!!

I won't be much online on next week so if any of you have emailed me regarding anything, please be patient on the reply. Cheers.

Enjoy!

Friday, October 20, 2006

OpenBSD Sguil Port

Nikns has submitted his OpenBSD Sguil ports, if you happen to deploy sguil on OpenBSD platform, give it a try and test, test and test so that Nikns can get it into OpenBSD ports tree and produces better and stable sguil port since it relies on many other applications as well where Nikns has ported. It should be working on OpenBSD 4.0 or Current.

The detail is here.

I'm currently installing OpenBSD using snapshot just to test the port, hopefully I can produce feedback when possible.

Thanks Nikns for his effort to create OpenBSD Sguil Port, Ch33rs!!!!!

Enjoy :]

Bro-IDS v1.2

For people who doesn't notice, Bro-IDS v1.2 is released, the major improvement should be the dynamic protocol detection, I can't really comment about it yet since I'm not getting into it yet. Other than that, there are lots of features and bugfixes been done in this latest version and you can find the changelogs here. If you want to know more about dynamic protocol detection, you can check this out.

Since I have Bro-IDS v1.1 running, surprisingly upgrading to version 1.2 can be done in a glance, just untar 1.2 source once you download it, and run the common steps - configure -> gmake && gmake install and you are done. I have no problem at all upgrading it to 1.2 on my FreeBSD box.

We all know Bro-IDS is not as popular as snort, however it is one of obvious alternative if you want to deploy network IDS since not many Open Source NIDS projects survive long enough as lots of efforts needed to produce solid NIDS.

Prelude is long gone for its NIDS feature, it is now more of SIM instead.

To Bro-IDS development team, you guys just rox!

Cheers :]

Wednesday, October 18, 2006

Good Link Indeed

Thanks to the anonymous reader who commented on my previous blog post and also posted a good link regarding squid+clamav+adzapper setup -

http://www.kernel-panic.it/

The link also contains various kind of tutorials especially on OpenBSD while not many but with good quality write up. Check it out!

Enjoy :]

Tuesday, October 17, 2006

Dansguardian+ClamAV+Squid

After digging all the possible content filtering solutions, I decided to give dansguardian a try, the interesting part of dansguardian is that it plays well with other open source applications such as clamAV and squid proxy, by integrating these two applications into dansguardian, you can easily setup your proxy with AntiVirus filtering and deploying powerful access control list to tighten your network access. Since most of the desktop users are not aware of network threats, this can serve as the platform to minimize the risk and saving users from the bad day.

Since I used to write lots of technical stuffs on my blog, however for this setup, I decide to write more comprehensive guide and put it up online to share with everyone, it does take some times to figure out most of the things and I seriously thank to chflags who has offered his much helps and times. Big credits to him and I really appreciated for the knowledge sharing from him.

For people who are interested on setting this up, you can download the guide at

http://www.dissectible.org/anonymous/Misc/Dgn-Clam-Squid.pdf

Any inputs and comments are welcomed, I hope you find it useful.

P/S: The setup is on FreeBSD platform, it shouldn't be vary too much from OpenBSD platform except for the dansguardian installation part where you will have to install from source on OpenBSD.

Enjoy (;])

Friday, October 13, 2006

Helix Live CD - Ntfs RW Support

The latest Helix Forensic Live CD is just released not long time ago, I always love it for the ease of use for Forensic Practioner. This release includes few interesting features that you can find here.

Instead of using captive for NTFS rw capability, now they are using ntfs-3g which is this. The ntfs-3g is better and clean tool to acces NTFS file system. While most people have problem with their Windows boxen but need to access the NTFS file system to retrieve the data, Helix seriously provides a very good solution now. Here's my testing on it.

I booted the Helix Live CD on my Windows box and choose gui(which is default), and you will see the XFCE desktop. I setup the network configuration by using the Netword Card Configuration which under Network in Helix Menu. Then I first enable ssh sever by clicking on Helix Menu -> Services -> Start SSH server, I will have to set the password for user - knoppix and I'm good to go, then I login to Helix via my FreeBSD workstation -

[root@trinity /nsm]# ssh knoppix@192.168.0.195
The authenticity of host '192.168.0.195 (192.168.0.195)' can't be established.
DSA key fingerprint is ac:ac:3b:40:23:73:90:2e:36:d3:ea:c4:1b:0e:eb:55.
Are you sure you want to continue connecting (yes/no)? yes
Warning: Permanently added '192.168.0.195' (DSA) to the list of known hosts.
Password:
Welcome to Helix (Kernel 2.6.14-9)

[knoppix (~)]$ su

Checking the file system that mounted on boot -

[root (knoppix)]# cat /etc/fstab
proc /proc proc defaults 0 0
sysfs /sys sysfs noauto 0 0
/dev/pts /dev/pts devpts mode=0622 0 0
/dev/cdrom /media/cdrom0 udf,iso9660 user,noauto 0 0
/dev/fd0 /media/floppy0 auto rw,user,noauto 0 0
# Added by HELIX
/dev/hda1 /media/hda1 vfat ro,noauto,users,noexec,nodev,noatime,umask=000,shortname=mixed,quiet 0 0
# Added by HELIX
/dev/hda5 /media/hda5 vfat ro,noauto,users,noexec,nodev,noatime,umask=000,shortname=mixed,quiet 0 0
# Added by HELIX
/dev/hda6 /media/hda6 ntfs ro,noauto,users,noexec,nodev,noatime,ro,umask=000 0 0

I have 3 partitions of which hda6 is using NTFS file system, then I can remount with read write capability by executing

[root (knoppix)]# ntfs-3g /dev/hda6 /media/hda6 -o force

Now I can read NTFS file system which is under /media/hda6

[root (knoppix)]# ls -la /media/hda6
total 371202
-rw------- 2 root root 32666 May 12 22:34 Cool-Ethereal-screenshot.PNG
-rw------- 2 root root 387584 Jul 26 01:29 Enterprise-Network-4.vsd
-rw------- 2 root root 421888 Jul 26 22:20 Enterprise-Network-6.vsd
-rw------- 2 root root 1655134 Apr 20 2005 GCIA.Silver.hi.eps
-rw------- 2 root root 1703856 Apr 12 2005 GCIA.Silver.hi.res.tif
-rw------- 1 root root 24498 Aug 22 05:18 ackcmd.zip
-rw------- 1 root root 62464 Jul 24 13:50 example.vsd
-rw------- 2 root root 1621662 Apr 21 2005 gcia_logos_silver.zip
-rw------- 1 root root 59767 May 24 15:37 hexquiz.pdf
-rw------- 2 root root 60636 May 24 15:37 hexquiz_answers.pdf

I can even delete one of the file since I have write permission -

[root (knoppix)]# rm -rf /media/hda6/hexquiz.pdf

[root (knoppix)]# ls -la /media/hda6/h*
-rw------- 2 root root 60636 May 24 15:37 /media/hda6/hexquiz_answers.pdf

It's gone. Now I can umount it with fuse :]

[root (knoppix)]# fusermount -u /media/hda6

This is neat indeed. Have fun with Helix Live CD.

Cheers (;])

FreeBSD - Lets BuRN!

I never burn any iso image using my thinkpad X41 laptop and just try yesterday when burning the new helix liveCD iso, seems not hard with cdrecord, here's how I do it,

[root@trinity ~]# cdrecord -scanbus
Cdrecord-Clone 2.01 (i386-unknown-freebsd6.1) Copyright (C) 1995-2004 Jörg Schilling
Using libscg version 'schily-0.8'.
scsibus0:
0,0,0 0) 'IBM ' 'CD-RW/DVD-ROM ' 'H.2E' Removable CD-ROM
0,1,0 1) *
0,2,0 2) *
0,3,0 3) *
0,4,0 4) *
0,5,0 5) *
0,6,0 6) *
0,7,0 7) *

[root@trinity ~]# cdrecord -v -pad \
speed=2 dev=0,0,0 /nsm/i-Iso/Helix_V1.8-10-05-2006.iso
cdrecord: No write mode specified.
cdrecord: Asuming -tao mode.
cdrecord: Future versions of cdrecord may have different drive dependent defaults.
cdrecord: Continuing in 5 seconds...
Cdrecord-Clone 2.01 (i386-unknown-freebsd6.1) Copyright (C) 1995-2004 Jörg Schilling
TOC Type: 1 = CD-ROM
scsidev: '0,0,0'
scsibus: 0 target: 0 lun: 0
Using libscg version 'schily-0.8'.
SCSI buffer size: 64512
atapi: 0
Device type : Removable CD-ROM
Version : 0
Response Format: 2
Capabilities :
Vendor_info : 'IBM '
Identifikation : 'CD-RW/DVD-ROM '
Revision : 'H.2E'
Device seems to be: Generic mmc2 DVD-ROM.
Current: 0x000A
Profile: 0x0010
Profile: 0x000A (current)
Profile: 0x0009
Profile: 0x0008
Using generic SCSI-3/mmc CD-R/CD-RW driver (mmc_cdr).
Driver flags : MMC-2 SWABAUDIO BURNFREE
Supported modes: TAO PACKET SAO SAO/R96P SAO/R96R
Drive buf size : 1421312 = 1388 KB
FIFO size : 4194304 = 4096 KB
Track 01: data 698 MB padsize: 30 KB
Total size: 802 MB (79:27.92) = 357594 sectors
Lout start: 802 MB (79:29/69) = 357594 sectors
Current Secsize: 2048
ATIP info from disk:
Indicated writing power: 3
Reference speed: 6
Is not unrestricted
Is erasable
Disk sub type: High speed Rewritable (CAV) media (1)
ATIP start of lead in: -11635 (97:26/65)
ATIP start of lead out: 359849 (79:59/74)
1T speed low: 4 1T speed high: 10
2T speed low: 4 2T speed high: 0 (reserved val 6)
power mult factor: 1 5
recommended erase/write power: 3
A1 values: 24 1A BC
A2 values: 26 B2 26
Disk type: Phase change
Manuf. index: 3
Manufacturer: CMC Magnetics Corporation
Blocks total: 359849 Blocks current: 359849 Blocks remaining: 2255
Starting to write CD/DVD at speed 4 in real TAO mode for single session.
Last chance to quit, starting real write 0 seconds. Operation starts.
Waiting for reader process to fill input buffer ... input buffer ready.
BURN-Free is ON.
Turning BURN-Free off
Performing OPC...
Starting new track at sector: 0
Track 01: 698 of 698 MB written (fifo 100%) [buf 99%] 4.1x.
Track 01: writing 30 KB of pad data.
Track 01: Total bytes read/written: 732317696/732348416 (357592 sectors).
Writing time: 1200.037s
Average write speed 4.0x.
Min drive buffer fill was 99%
Fixating...
Fixating time: 70.291s
cdrecord: fifo had 11535 puts and 11535 gets.
cdrecord: fifo was 0 times empty and 11115 times full, min fill was 81%.

Then I mount my cdrom and check if the image is written properly on CD,

[root@trinity ~]# mount -t cd9660 /dev/cd0 /mnt/cdrom

[root@trinity ~]# ls /mnt/cdrom
AutoPlay KNOPPIX autorun.inf helix.ico
EULA.pdf Language boot index.html
IR Static-Binaries helix.exe

It seems everything goes well, cheers to myself.

Enjoy ;]

Thursday, October 12, 2006

Real Rant

When will our .gov.my stop being defaced?

I hope someone can give me answer on this .....

No Cheers :[

Saturday, October 07, 2006

Security Implementation is not about BrandName

I have to write this since I feel sick with brand name products that kills my brain. Talking about network security implementation, we can always listen people who are brainless discussing about how powerful those commercial appliances - either firewall, ids or whatever commercial hype terms are. Those companies used to release old technologies with their powerful packaging idea. Due to that lots of enterprises start to believe and trust them for their network security deployment.

Outsourcing is another trend that follow up to provide all kind of network security services. Those third party vendors who provide the network security services also form alliance with the companies that selling their so called brand name security devices. We can see that this trend will be the future indeed.

Lots of enterprises start to buy in those vendors to plan and deploy their network security structure, and then hiring all the dumb system admin to maintain their workstation and fixing small network issues, and they can play blaming to the third party vendors if their security deployment is broken somewhere.

Now come back to the topic, yes and those third party vendors will deploy those branded network security devices such as ciscock, junipet, and so forth since those devices can do A to Z, but my point here should be no matter what kind of security devices you have, the problem occurs if you have faulty network security implementation. I do know those security service provider will plan properly so that they can maintain their business consistency. But I do believe one thing - trust your internal sysadmin and network admin when comes to network security implementation. They are the one who know and understand what is running in the network, yeah you may tell me how about internal threats however this is not in my discussion here.

I'm open source centric person, but I just don't want to compare what open source security applications can do comparing to commercial branded name applications here. It will only create stupid flame war which I don't want, I'm just try to awake those dumbass(enterprises?) when comes to implement your network security.

- Think brain > brand

- Network & Service profiling(Trust your internal sysadmin and netadmin for this)

- Plan, plan & more plans(Discussion of your tech team with vendors maybe)

- Implementation & Deployment(Never ask for what kind of brand name devices that they can provide, asking what kind of security implementations they can deploy which suits your network)

- Never trust non-tech people to discuss with security service providers - they are the dumbass!

- No undertable - corruption used to happen because those dumbass will accept money from security provider for their buy in especially if those dumpass are one of decision maker and hey, that's easy money.

- Don't think buying 100K branded firewall can cover your ass!

- Improve over time based on the changes of your network architectures

I have seen and talk to lots of technical department managers out there, apparently they are coming from management or business background, ouch! You shouldn't have hired this kind of people at the first place. Those talkers can't do all the tech stuffs but bullshiting a lot. Kick them out of the room, please!!!!! By the way don't tell me you have CISSP, I don't bother.

To those people who insist believe a very good brand name products can survive todays threats, I can tell you that yeah, the products may not suck but you suck of believing those marketing hypes.

For those people who work as real sysadmin|netadmin|secadmin, saluteeeeee!

Happy Ranting :]

Thursday, October 05, 2006

Argus - Read This!!!!!

For people who plan to use argus and don't know what it actually is -

http://www.rfc-editor.org/rfc/rfc2724.txt


Lets RTFM

For people who want to know how argus can do in Network Security Context -

http://www.qosient.com/argus/security.htm

For people who want to try out latest argus -

ftp://qosient.com/dev/argus-3.0

Enjoy :)

Argus-3.0(dev) - Ragraph

Argus 3.0 is in active development, I guess most of argus users should give the development version a try since there are a lot of changes from 2.0 to 3.0, by the way tools like ratop, racluster, ragraph and etc are added. I have no problem to get it compiled however I have problem when I run ragraph, anyway I just solve it with pkg_add since it requires certain perl module to work.

shell>pkg_add -r p5-RRDTool-OO

This is just note to myself in case I have forgotten next time, by the way I think argus 3.0 will be in FreeBSD port when it is released.

Cheers to all arguser :]

P/S: Feel free to contribute to argus wiki page -
http://www.vorant.com/nsmwiki/index.php?title=Argus

Wednesday, October 04, 2006

Bittwiste - Revision

Talking about editing pcap files, I always have this problem where I want to change the IP address to another IP address, for example I want to change 1.2.3.4 to 192.168.48.21, I can do it easily if it is only fewer records or small pcap files with netdude. However I always have problem with this kind of Pcap files where IP 1.2.3.4 is in the source and destination IP field(bidirectional for example TCP connections), if I use netdude to change the IP address by highlighting the pcap records, all the source IP will be changed to the same as 1.2.3.4 which I don't want. In TCP connections, we usually have this kind of connections,

1.2.3.4 -> x.x.x.x
x.x.x.x -> 1.2.3.4
1.2.3.4 -> x.x.x.x

So if I use netdude, it will becomes -

192.168.48.21 -> x.x.x.x
192.168.48.21 -> 1.2.3.4
192.168.48.21 -> x.x.x.x

This is very inconvinient and I have to manually change either the source and destination IP. I feel that there's lack of tool that can do the thing I want and fortunately we have latest Bitwiste which able to do this type of thing.

Let's say now I have this Pcap file called TCP-Learning.pcap -

shell>tcpdump -nr TCP-Learning.pcap

reading from file TCP-Learning.pcap, link-type EN10MB (Ethernet)
17:19:46.623049 IP 222.64.79.60.3493 > 1.2.3.4.80: S 676482397:676482397(0) win 65535
17:19:46.623101 IP 1.2.3.4.80 > 222.64.79.60.3493: S 814542684:814542684(0) ack 676482398 win 5840
17:19:46.834035 IP 222.64.79.60.3493 > 1.2.3.4.80: . ack 1 win 65535
17:19:46.882274 IP 222.64.79.60.3493 > 1.2.3.4.80: P 1:313(312) ack 1 win 65535
17:19:46.882323 IP 1.2.3.4.80 > 222.64.79.60.3493: . ack 313 win 6432
17:19:46.883334 IP 1.2.3.4.80 > 222.64.79.60.3493: P 1:615(614) ack 313 win 6432
17:19:47.184978 IP 222.64.79.60.3493 > 1.2.3.4.80: . ack 615 win 64921
17:19:53.598808 IP 222.64.79.60.3493 > 1.2.3.4.80: P 313:625(312) ack 615 win 64921
17:19:53.599825 IP 1.2.3.4.80 > 222.64.79.60.3493: P 615:1229(614) ack 625 win 7504
17:19:53.927832 IP 222.64.79.60.3493 > 1.2.3.4.80: . ack 1229 win 64307
17:20:09.744646 IP 1.2.3.4.80 > 222.64.79.60.3493: F 1229:1229(0) ack 625 win 7504
17:20:09.946046 IP 222.64.79.60.3493 > 1.2.3.4.80: . ack 1230 win 64307
17:20:14.316555 IP 222.64.79.60.3493 > 1.2.3.4.80: R 625:625(0) ack 1230 win 0

Now I want to change 1.2.3.4 either in source or destination IP field to 192.168.48.21, what I can do is just one liner with bitwiste,

shell>./bittwiste -I ./TCP-Learning.pcap -O TCP-Learning-edited.pcap -T ip -s 1.2.3.4:192.168.48.21 -d 1.2.3.4:192.168.48.21

shell>tcpdump -nr TCP-Learning-edited.pcap
reading from file TCP-Learning.pcap, link-type EN10MB (Ethernet)
17:19:46.623049 IP 222.64.79.60.3493 > 192.168.48.21.80: S 676482397:676482397(0) win 65535
17:19:46.623101 IP 192.168.48.21.80 > 222.64.79.60.3493: S 814542684:814542684(0) ack 676482398 win 5840
17:19:46.834035 IP 222.64.79.60.3493 > 192.168.48.21.80: . ack 1 win 65535
17:19:46.882274 IP 222.64.79.60.3493 > 192.168.48.21.80: P 1:313(312) ack 1 win 65535
17:19:46.882323 IP 192.168.48.21.80 > 222.64.79.60.3493: . ack 313 win 6432
17:19:46.883334 IP 192.168.48.21.80 > 222.64.79.60.3493: P 1:615(614) ack 313 win 6432
17:19:47.184978 IP 222.64.79.60.3493 > 192.168.48.21.80: . ack 615 win 64921
17:19:53.598808 IP 222.64.79.60.3493 > 192.168.48.21.80: P 313:625(312) ack 615 win 64921
17:19:53.599825 IP 192.168.48.21.80 > 222.64.79.60.3493: P 615:1229(614) ack 625 win 7504
17:19:53.927832 IP 222.64.79.60.3493 > 192.168.48.21.80: . ack 1229 win 64307
17:20:09.744646 IP 192.168.48.21.80 > 222.64.79.60.3493: F 1229:1229(0) ack 625 win 7504
17:20:09.946046 IP 222.64.79.60.3493 > 192.168.48.21.80: . ack 1230 win 64307
17:20:14.316555 IP 222.64.79.60.3493 > 192.168.48.21.80: R 625:625(0) ack 1230 win 0

This is clean and neat, thanks to Addy(author of bittwist) who has added this feature for the ease of use. Feel free to download it at here and give it a try.

What a powerful pcap editing tool!!!!!

Enjoy (:])

Crime Detections

While watching news on TV yesterday night, I were surprised that our police enforcement don't have computer system that keeping track of criminal activities. With this kind of criteria, I'm wondering how our security is guaranteed in such a way, the criminal profiling is handled in very inefficient ways which is decentralized and by each branches in different locations.

And now only they come to realized that they need to have centralized management and start to build the database system, this can be considered as good new since it is never too late to do it while other countries have this kind of system ages ago.

I think with this kind of system, the correlations can be done and it is time saver as well since each branches doesn't have to take much times to query the records and profiles of criminals. The information sharing within each branches will help and all the police stations are now merged into empowered body even they are all separated physically.

They should be sharp in crime detections with this kind of deployment. By the way I'm wondering when the system will be completely built while the project is started on December of this year if I'm not mistaken.

Cheers :]

Sunday, October 01, 2006

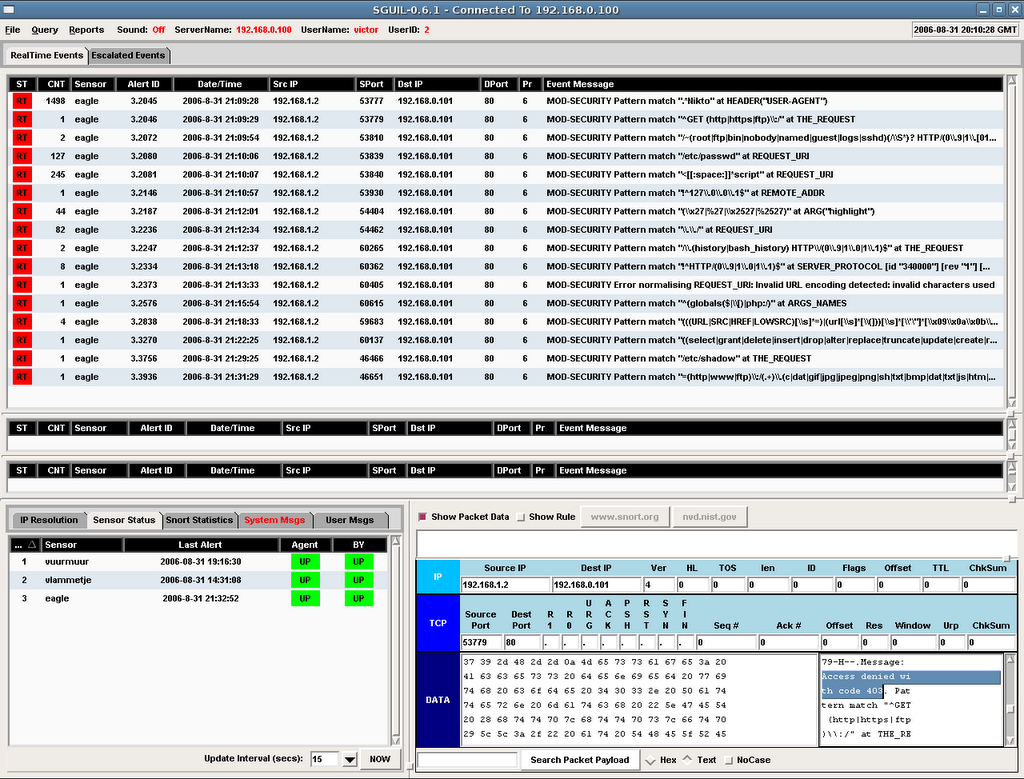
ModSec2Sguil Screenshots

I just hacked into Victorj's blog and stole his screenshot so that I can share it with everyone, I don't think he will know it since I can easily bypass his IDS. Enjoy the Mod_Security Logs in Sguil!!!!!


Oops, I just forgot he deployed NSM instead of IDS only, damn!!!!!

Enjoy :]

Saturday, September 30, 2006

PgOSS Meetup - Continued

Thanks to surface for recording the talk in mp3 format so that we can share the PgOSS presentation with others. Here's the second presentation that done by Vicky -

http://mysurface.no-ip.org/download/02vick.mp3

And for anyone who stay around Pulau Penang, and you would like to join us in the next meetup, you can find the information @t

http://foss.org.my/projects/meetups/2006-09/pgoss/

By the way I'm looking for anyone who would like to share their OSS expereience and skills in the meetup, please email me and I would like to hear from you. My email is as the same as always geek00L[at]gmail.com.

Enjoy :]

PgOSS Meetup

This is the first official meetup for Penang Open Source Software Meetup, you can find the initial meetup announcement @t

http://my.opera.com/mysurface/blog/show.dml/484686

http://aizatto.com/blog/archives/180

The meetup is over, I know many of you are looking for me in the meetup since I'm one of organizer, however I were not be able to attend the meetup due to some personal issue, fortunately there are aizat and surface who are willing to help, aizat was down from Kuala Lumpur to Penang and I'm glad that he makes his way here :)

Anyway thanks to everyone that coming to the meetup, especially Dr. Dhanesh who has helped organizing the meetup.

I hope that we can organize the meetup again next month and looking forward to see everyone in the meetup if possible. For more information regarding the meetup, I think aizat and surface will blog the wrap-up.

This is not a hardcore OSS meetup, and PgOSS guys have captured the scene to share and you can download it via

http://mysurface.no-ip.org/download/01aizat.mp3

Have fun with OSS!!!!!

Cheers :]

P/S: For whoever think I'm coming, I'm cheating for good intention :P

Thursday, September 28, 2006

Snort and ModSec2Sguil

I know I haven't been posting in my blog for quite sometimes, lots of things in my mind that I have to get it done. However for those who is snort lover, the snort 2.6.1 beta2 is already out for quite sometimes, and I just noticed it. Lots of decoders are added to solve the detection issue. I hope I can spare my time to test those preprocessors but this is not the case, maybe next month or when snort 2.6.1 releases.

For Sguil Lovers, check out -

http://www.inliniac.net/blog/?p=43


Mod_Security Logs now can be managed and analyzed thru Sguil, thanks to Victorj who has written ModSec2Sguil. I hope it will be added as extra features for Sguil. This is good news for serious and heavy users of Mod_Security. You can have centralized center to perform analysis on Mod_Sec Logs now.

I will try my best to write more about NSM stuffs when I have time, currently I'm still testing OpenBSD PF layer 2 filtering stuffs and hopefully I can blog about it when I have time.

Cheers :]

Saturday, September 23, 2006

HITB Conference 2006

Finally everything is over, I'm glad that the training class was going fine for the first time me and mel conducting it together.

For the Capture The Flags Hacking Competition. While it is not perfect, we all learnt something from the setup and improvement can be done in future, thanks to all the CTF Crews, speakers who submitted the daemons as well as the volunteers who doing the cabling job.

I don't have much time to get into any speaker's talk but Philippe Biondi, since I use Scapy a lot and his talk was really interesting including the tricks and tips on toying with IPv6.

Finally thanks to all the HITB members to make this conference successful.

Again, I'm glad to work with you guys - mel, takizo, rd, xwings, ditesh, adli, y0muds and some other cool guys. You all just r0x0r5!!!!!

Special thanks to mel for his clothes, takizo who offers me his place to stay while I'm homeless..... and his kindness for donating so much $$$$$ to NCC.

Cheers :]

Saturday, September 16, 2006

Short Note

FreeBSD gtk theme for user is located at ~/.gtk-2.0 but the global one is at /usr/X11R6/share/themes. Change the theme as you wish or you can download those themes from whatever look - gnome-look, kde-look, and so forth.

By the way, for user who are not using gnome or kde, if you want to change your gtk setting, try

http://plasmasturm.org/code/gtk-chtheme/


Nice little tool indeed.

Anyway I will be heading to Kuala Lumpur for HackInTheBox Conference, geek party will be launched soon!!!!!

Enjoy :]